Most enterprise networks have accumulated things nobody would design into a new network: an old management interface, a temporary access rule that became permanent, devices running software that everyone agrees should have been upgraded. Keeping services running takes priority, and meanwhile the backlog of technical debt grows.
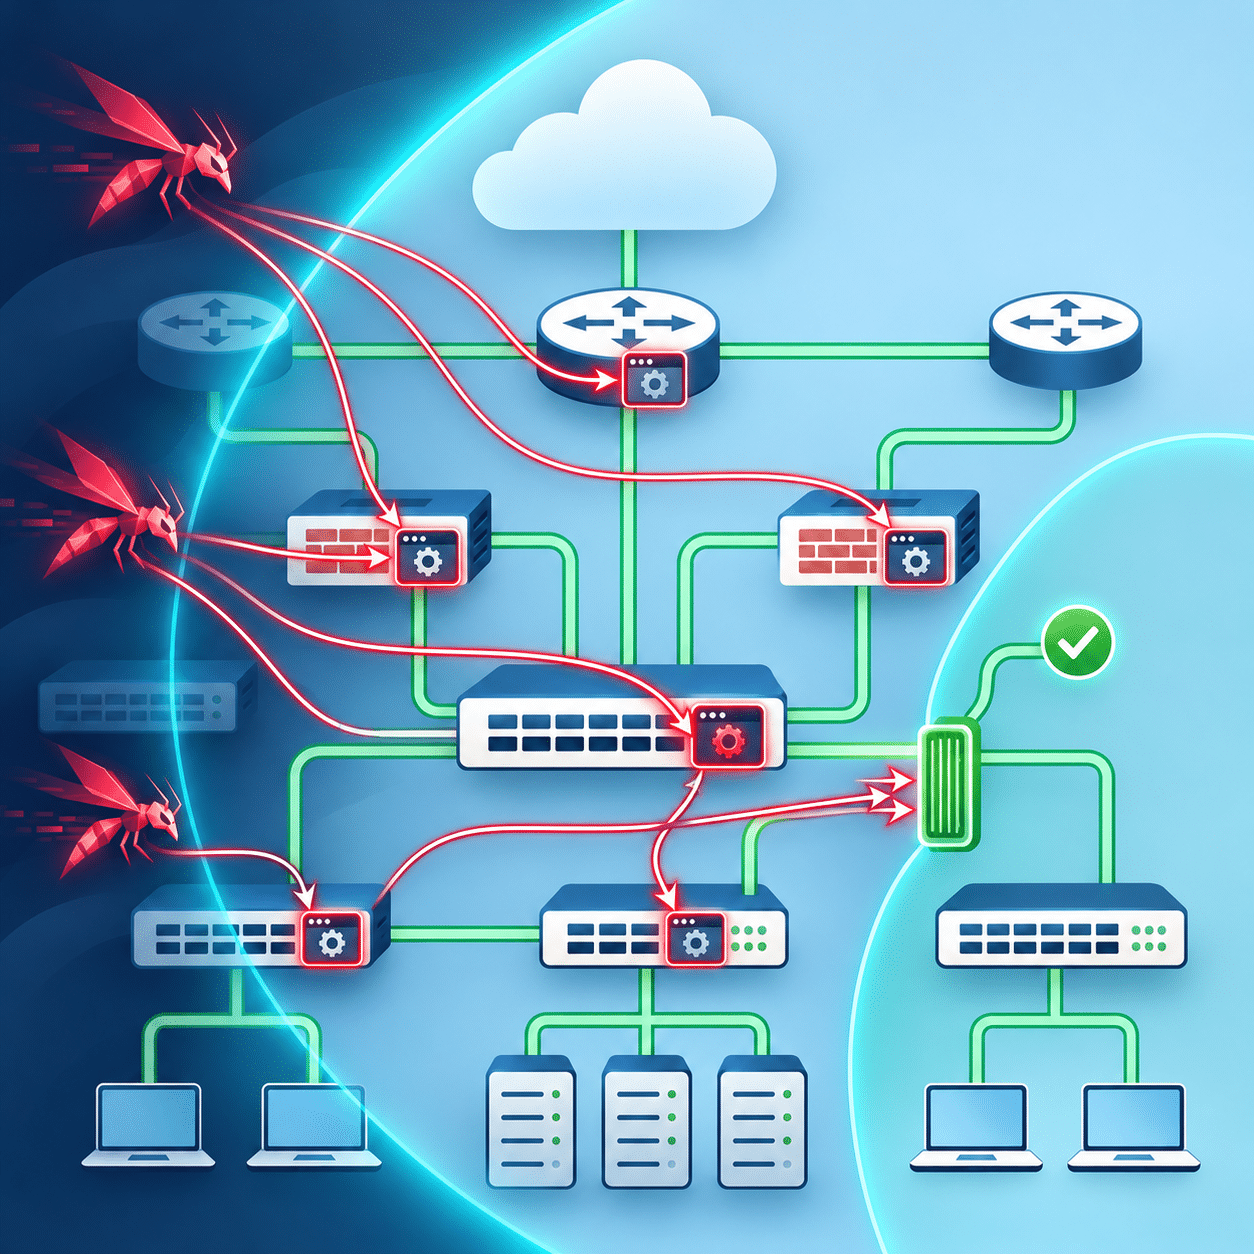
On November 13, the FBI issued a warning that underlines how untenable that backlog has become. Attackers are using ARTEX, an agentic penetration-testing framework, to automate reconnaissance, exploitation, and subsequent intrusion activity. Some attacks progressed from initial targeting to privileged access in under three hours.
Anthropic’s Mythos research demonstrated AI’s ability to discover vulnerabilities and assemble working exploit chains. To my mind, ARTEX represents that demonstration turning into production capability in operational attacks: more adversaries able to investigate more targets and connect weaknesses faster.
Security through obscurity was always a bad idea. But the time and expertise required to investigate obscure systems did impose a cost-based friction that made it so attackers had to prioritize high-value target. However, agentic tools have significantly eroded that friction. Assuming nobody will find an exposed service or understand an unusual configuration has now become an exceptionally expensive bet.
Dealing with brownfield network realities
Telling network teams to “patch everything immediately” doesn’t work in practice. A brownfield, multi-vendor network contains different upgrade procedures, service dependencies, unsupported devices, and configurations shaped by years of operational decisions. An urgent security change can still interrupt patient care, production, or financial transactions.
Nor does patching alone answer the ARTEX warning. The FBI also calls for restricting management interfaces, reducing external exposure, and tightening application permissions and credential monitoring. Agentic attacks exploit weaknesses across those boundaries.
What has become non-negotiable is an automated, continuous operating discipline: know the network’s OS, configuration, and operational state; identify stale settings and drift; determine vulnerability relevance; apply patches or compensating controls; verify the result.
That work can no longer be the domain of manual investigation and execution.
A full-stack approach to meeting the ARTEX moment
Gluware addresses this through a full-stack, intent-driven network automation platform built for multi-vendor environments. Its maintained foundations connect discovery, configuration management, software lifecycle management, assessment, and orchestration.
Device Manager discovers and inventories devices and inspects their software and configuration state. Config Drift & Audit captures configuration and operational command results, compares snapshots, and checks required or forbidden conditions. Assessments can run on schedules, from syslog events, or through workflows. Teams can check whether yesterday’s hardening still holds after today’s emergency change.
Detection needs a path to correction. Config Model Editor (CME) defines intended configuration, previews differences against live devices, and applies modeled changes. Its separate state assessments support checks before and after provisioning. A stale access rule needs an approved replacement and verification that the resulting configuration behaves as intended.
Titan Exposure Management adds two connected capabilities. Exposure Analysis assesses CVEs against OS, configuration, and operational context without changing the network. This helps establish whether a vulnerability actually matters on a particular device. Exposure Remediation connects relevant findings to supported patches or compensating controls, with approvals, validation, and outcome verification.
OS Manager supplies approved-image catalogs and deployment plans, readiness validation, scheduling, and execution review. Network RPA coordinates these operations with configuration changes, separate assessments, and service-management processes such as ServiceNow approvals. This makes remediation a repeatable operational process that the team can improve and trust.
A Proof of Agentic Trust approach
Underneath these capabilities, DIAL, Gluware’s Device Interaction and Automation Layer, handles device-specific translation, normalization, and deterministic validation across supported CLI and API interfaces.
Not only is DIAL essential to sound automation, it’s also the foundation for ensuring proof of agentic trust. When Titan Exposure Management’s builder skills generate proposed changes to configuration intent models, a separate, independent skill subjects those proposals to technical validation that leverages DIAL’s dozen years and million-plus hours of engineering and corner case hardening to validate that configs will work.
Network automation is table stakes
There is no simplistic answer to agentic exploitation. But continuously discovering, assessing, correcting, and verifying network state is now a basic requirement for managing an enterprise network. ARTEX makes postponing that foundation much harder to justify.